Behavioral detection on your SIEM
Built by ARRTECH AI researchers working alongside SOC practitioners: rigorous methods from time-series, sequence, neural and graph analysis, engineered to be inspected and measured on your own telemetry before they go live.
How it works
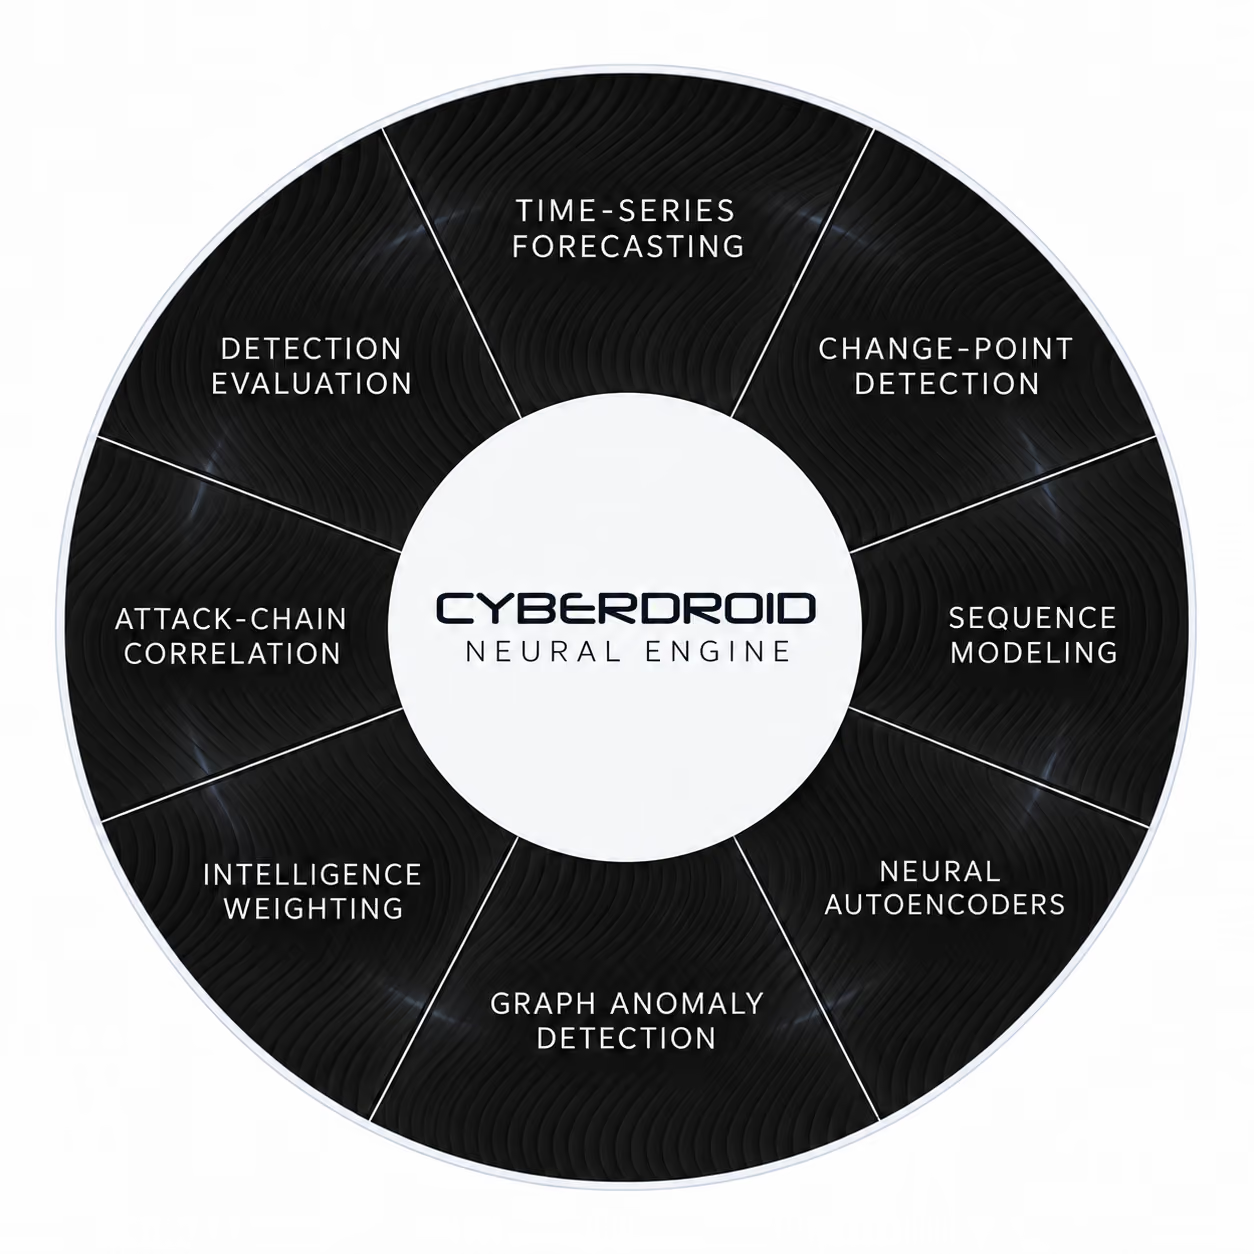
Cyberdroid AI Detection baselines every user, host and application against its own history and its neighbors, across identity, network, DNS, process and firewall telemetry. It shows the evidence behind every finding, so you understand behavior instead of receiving another score. Schedule a meeting and we will walk you through the workflow.
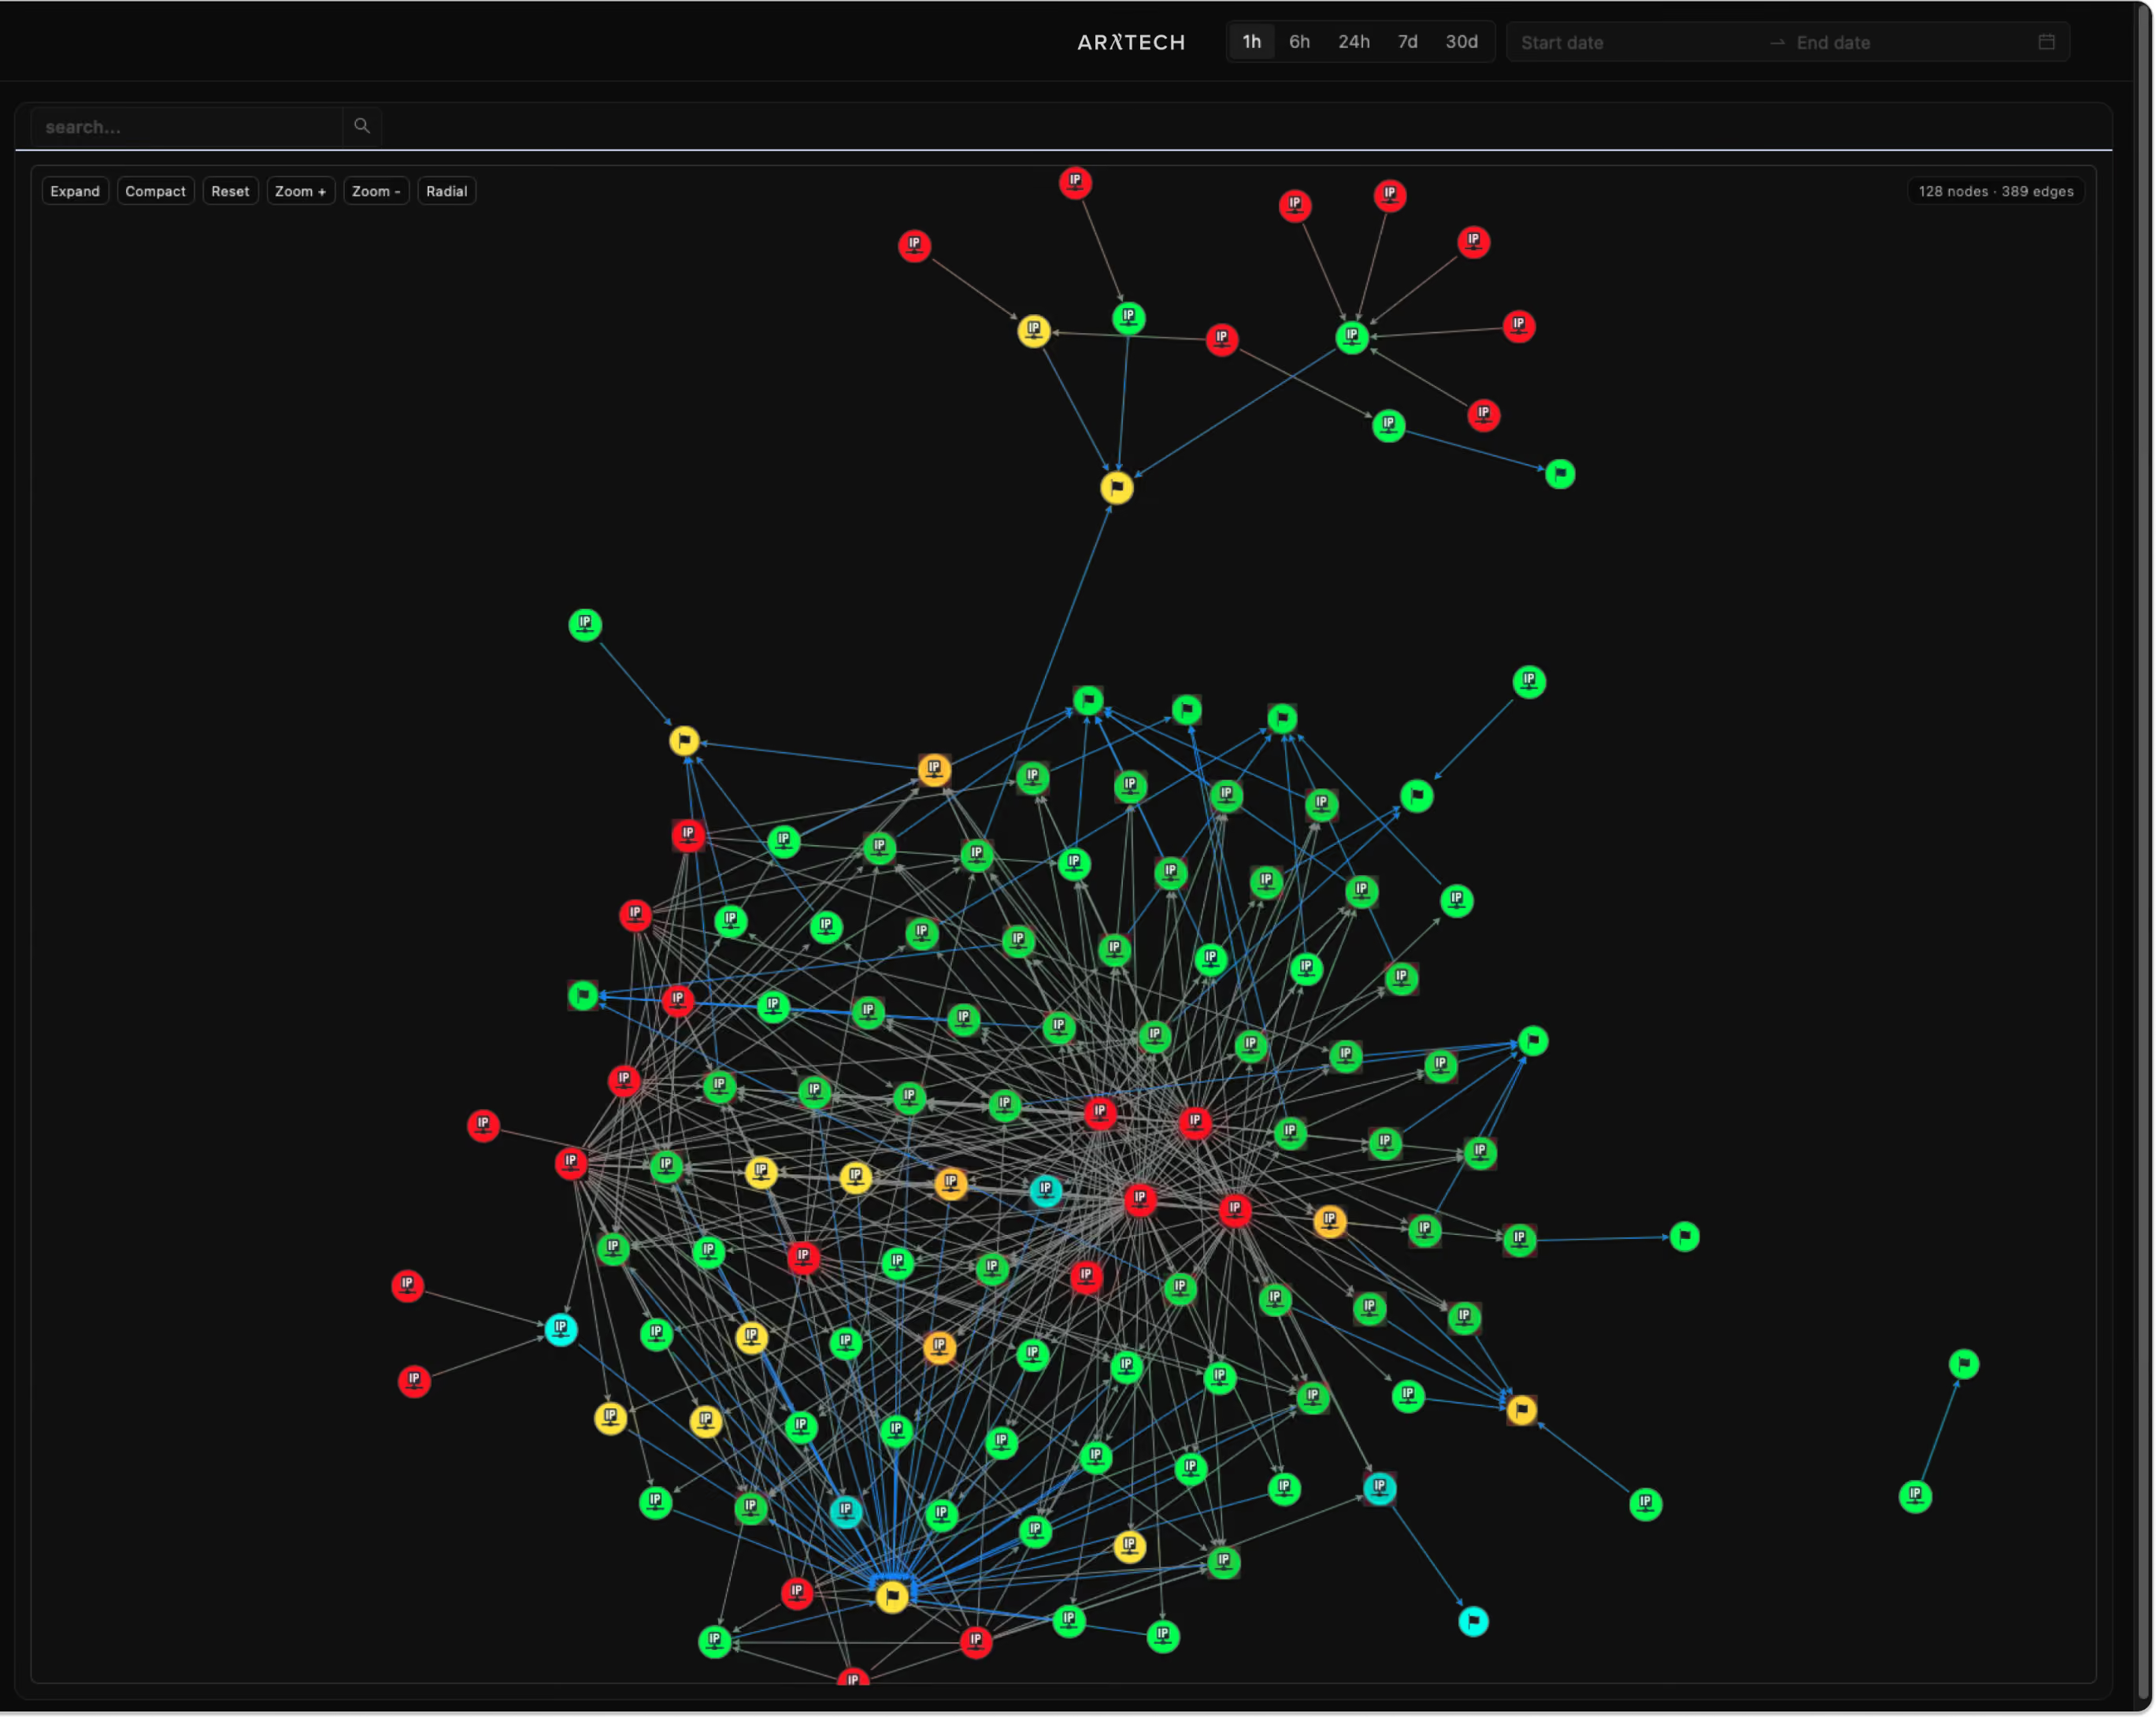
Atlas workspace: the relationships around every user, host and application, one hour of one estate
 Advantages
See why.
Every finding shows observed value, baseline, score and threshold, an evidence timeline, process lineage, corroborating findings, and the provenance, age and trust of the intelligence behind it. You see what supports a finding before you act, and a Markdown report exports into your case tool.
Behavior, not patterns.
Five analytics families ask whether an entity is behaving unusually against its history: time-series baselines, sequence and process novelty, a UEBA neural autoencoder, relationship-graph anomalies and known-threat intelligence, correlated into attack chains with MITRE context. It surfaces what pattern matching is not built to see.
Know the gaps.
Telemetry-health and schema-readiness checks run beside every detection output, and the Runtime workspace shows source availability and processing diagnostics. You know the difference between “nothing suspicious was found” and “the telemetry was incomplete”. Blind spots are found by the console, not by the incident.
Evolves under control.
21 ML detectors run disabled, in shadow or in production. Shadow findings take a separate channel, replay measures precision, recall, stability and volume per detector, and every promotion or rollback is recorded. New logic is proven on your data before it raises a production alert.
Touches nothing.
AI Detection deploys beside the SIEM and reads its newline-JSON export from a read-only share. It runs on CPUs in your environment, no GPU, and source logs stay separate from analytical output. No write access, no automated actor, and your telemetry stays where it is.
Requirements
ARRTECH SIEM, or a third-party SIEM with a supported export format. CPUs in your environment, no GPU. Sizing guidance on request.
Limits
AI Detection analyzes each hour after it closes, never blocks or changes anything in your estate, and treats a risk score as a prioritization aid, not a verdict.
