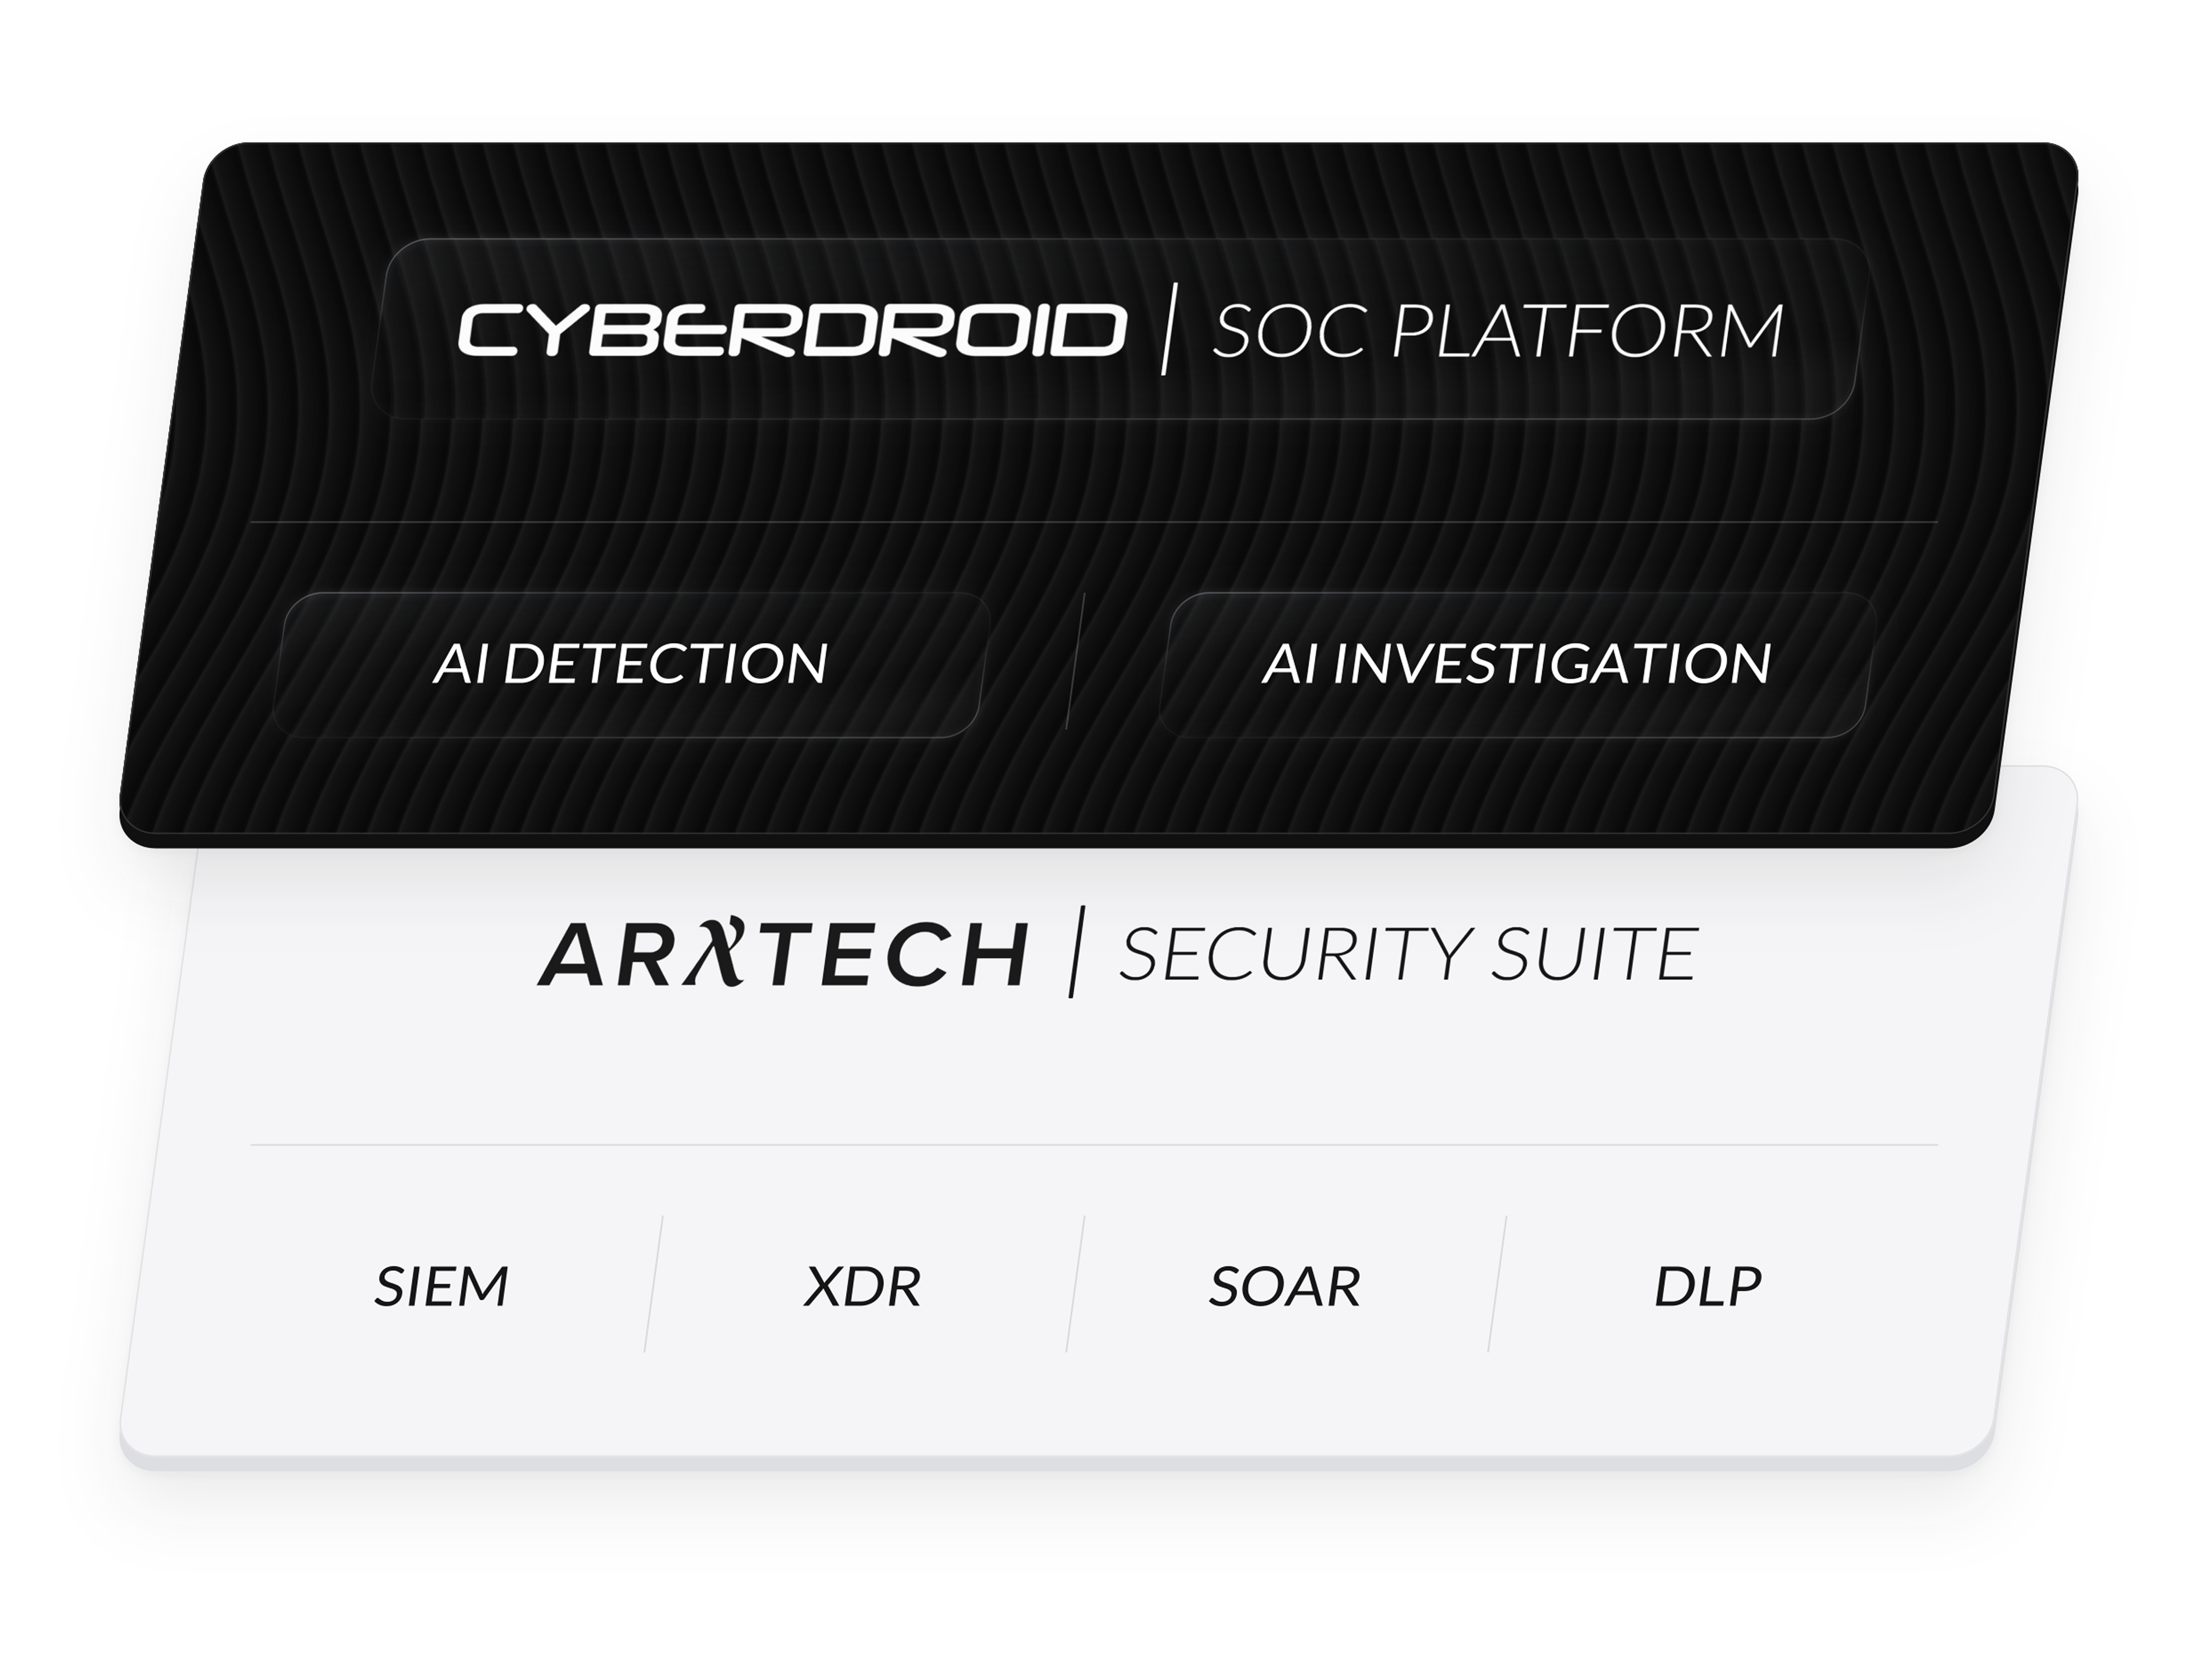
AI Layer
Amplifies SIEM.
A SIEM is required because nothing is detected that was not collected. It holds identity, network, DNS, process and firewall telemetry, most of it queried only after an alert. The AI layer reads that export in full, read-only. No endpoint software, nothing written back.
Amplifies XDR.
XDR and SIEM rules are required: known attacks must be caught as they happen. They find what was already described. The AI layer adds behavioral analytics: each user, host and application compared with its history and peers, across sources. Analysts see behavior no rule describes.
Amplifies SIEM search.
SIEM search is where analyst hours go: each alert means a person assembling context query by query. The AI layer investigates, read-only: it gathers evidence, tests the hypothesis and returns a reviewable case. Investigation is no longer rationed by analyst hours.
Amplifies SOAR.
SOAR and XDR response are required: containment must be immediate and repeatable. Whether AI should act is an open question. The AI layer cannot. It reports; a person approves; SOAR acts; every decision is recorded. Capacity is added; the estate gains no new actor.
Amplifies DLP.
DLP is required because data leaves through people. AI opens a new channel: the answer. Investigation results are the SOC’s most sensitive data. The AI layer extends disclosure control to its own answers: who may ask, who may receive, checked before and after rendering.
Products

Cross-source behavioral detection on your SIEM: identity, network, DNS, process and firewall telemetry, baselined against each entity’s own history.

Read-only investigation that turns Detection findings and SIEM alerts into reviewable cases, with Agent Gateway and Agent Desk included.