SIEM, SOAR and DLP on one console
Start with one
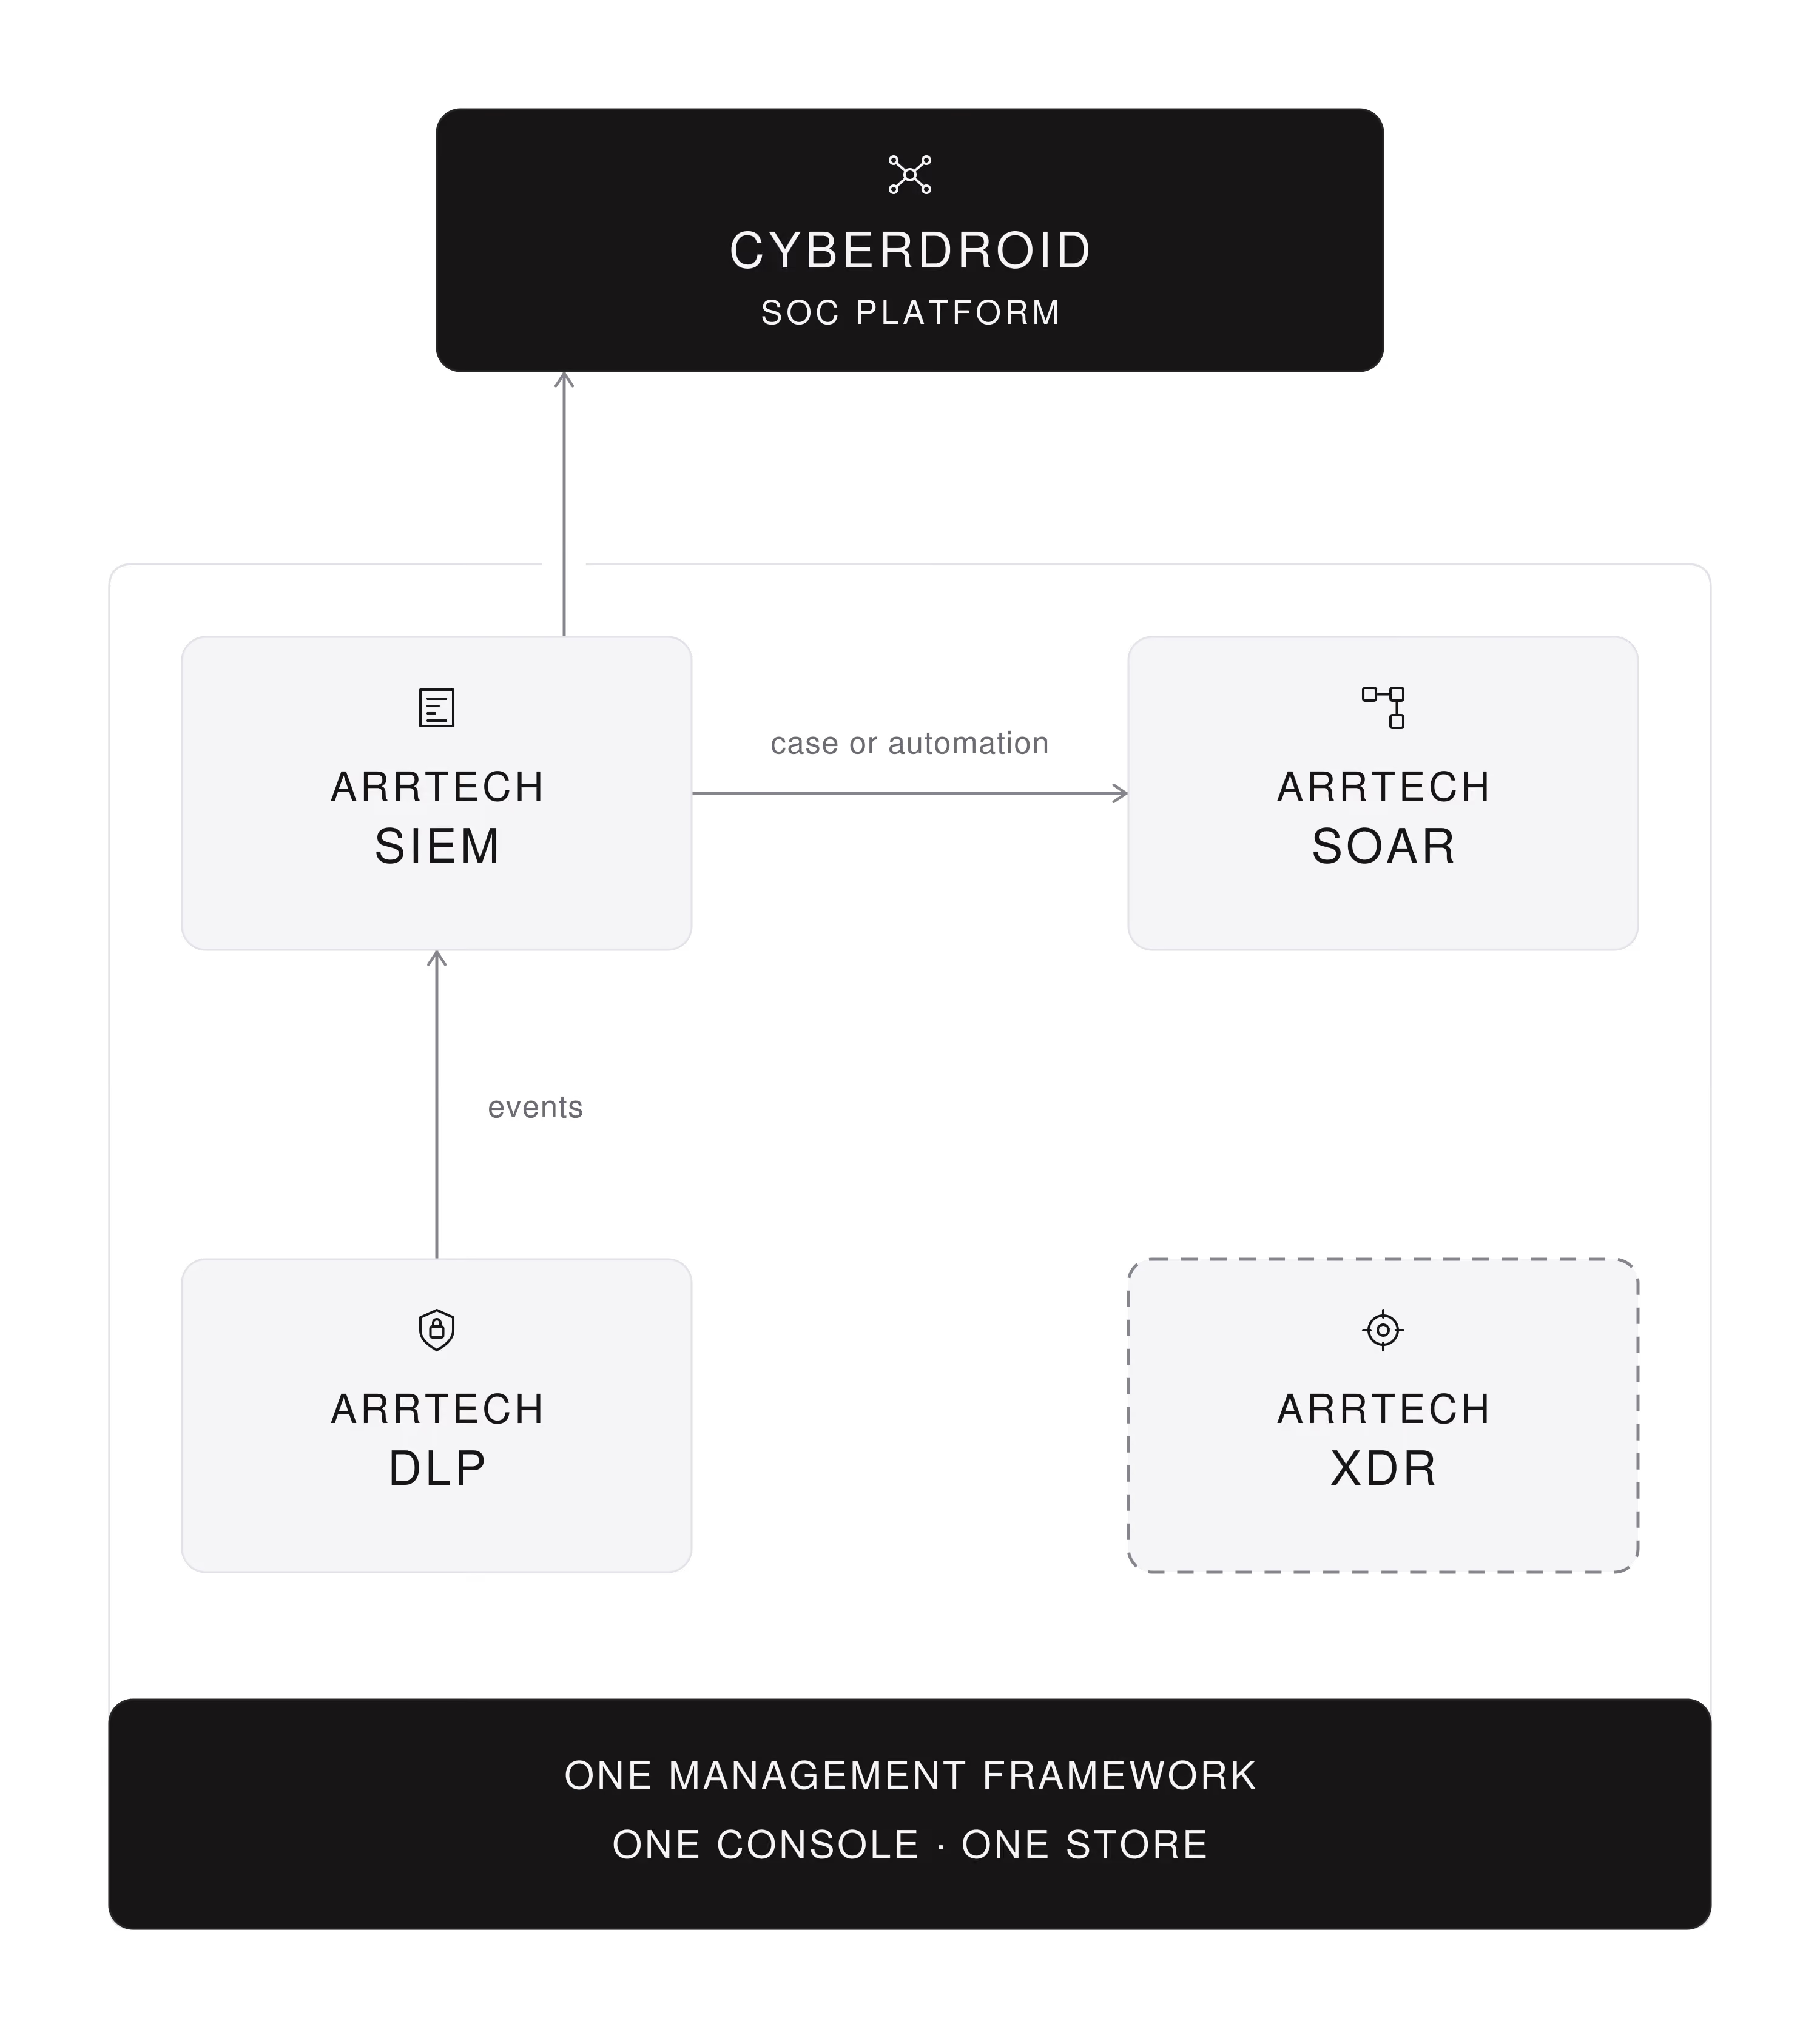
The ARRTECH Security Suite runs SIEM, SOAR and DLP on one console today and adds XDR in Q4 2026. You replace one tool at renewal and add the next without a second admin stack, so consolidation happens at your pace. A person approves what acts.
Why switch
Your pace.
Most estates run SIEM, SOAR and DLP from three vendors, each with its own console and agents. ARRTECH products share one management framework and one console. A Management Agent installs first and manages every product agent, so a second product adds no second admin stack.
Your incident.
A blocked upload, a firewall log and a sign-in are one incident, and usually three tools. ARRTECH DLP feeds its events to ARRTECH SIEM as a log source. A SIEM correlation alert opens an ARRTECH SOAR case or runs an automation from the alert action.
Your servers.
Most platforms hold your telemetry in their cloud. ARRTECH SIEM runs on Linux servers you own, licensed on daily volume with unlimited sources and agents. ARRTECH DLP deploys on premises, as SaaS, hybrid or multi-tenant for an MSSP. ARRTECH SOAR runs standalone or distributed.
Your evidence.
Lock-in is the price of most platforms. Every log the SIEM stores is hashed, signed, chained and timestamped daily. Any source exports with its certificate and a standalone verifier, so a third party checks it without ARRTECH. Each product has a REST API.
Your approval.
Platforms now promise to act at machine speed. An ARRTECH SOAR playbook pauses at an Operator node and a person picks from up to five options. ARRTECH DLP can ask a manager before releasing a file. The console records every login, search and configuration change.
Products

Collects, signs and correlates logs from more than 500 source types, with UEBA and graph analytics.
Learn more
Runs incident playbooks through API integrations, with a human decision built into the flow.
Learn more
Stops data leaving through endpoints, mail, web, shares, removable media and printers, at the kernel level.
Learn more