Skip to content
ARRTECH SIEM

Signed, searchable logs from every system

ARRTECH SIEM collects logs across the organization, signs each one as it is written and links related events into incidents.
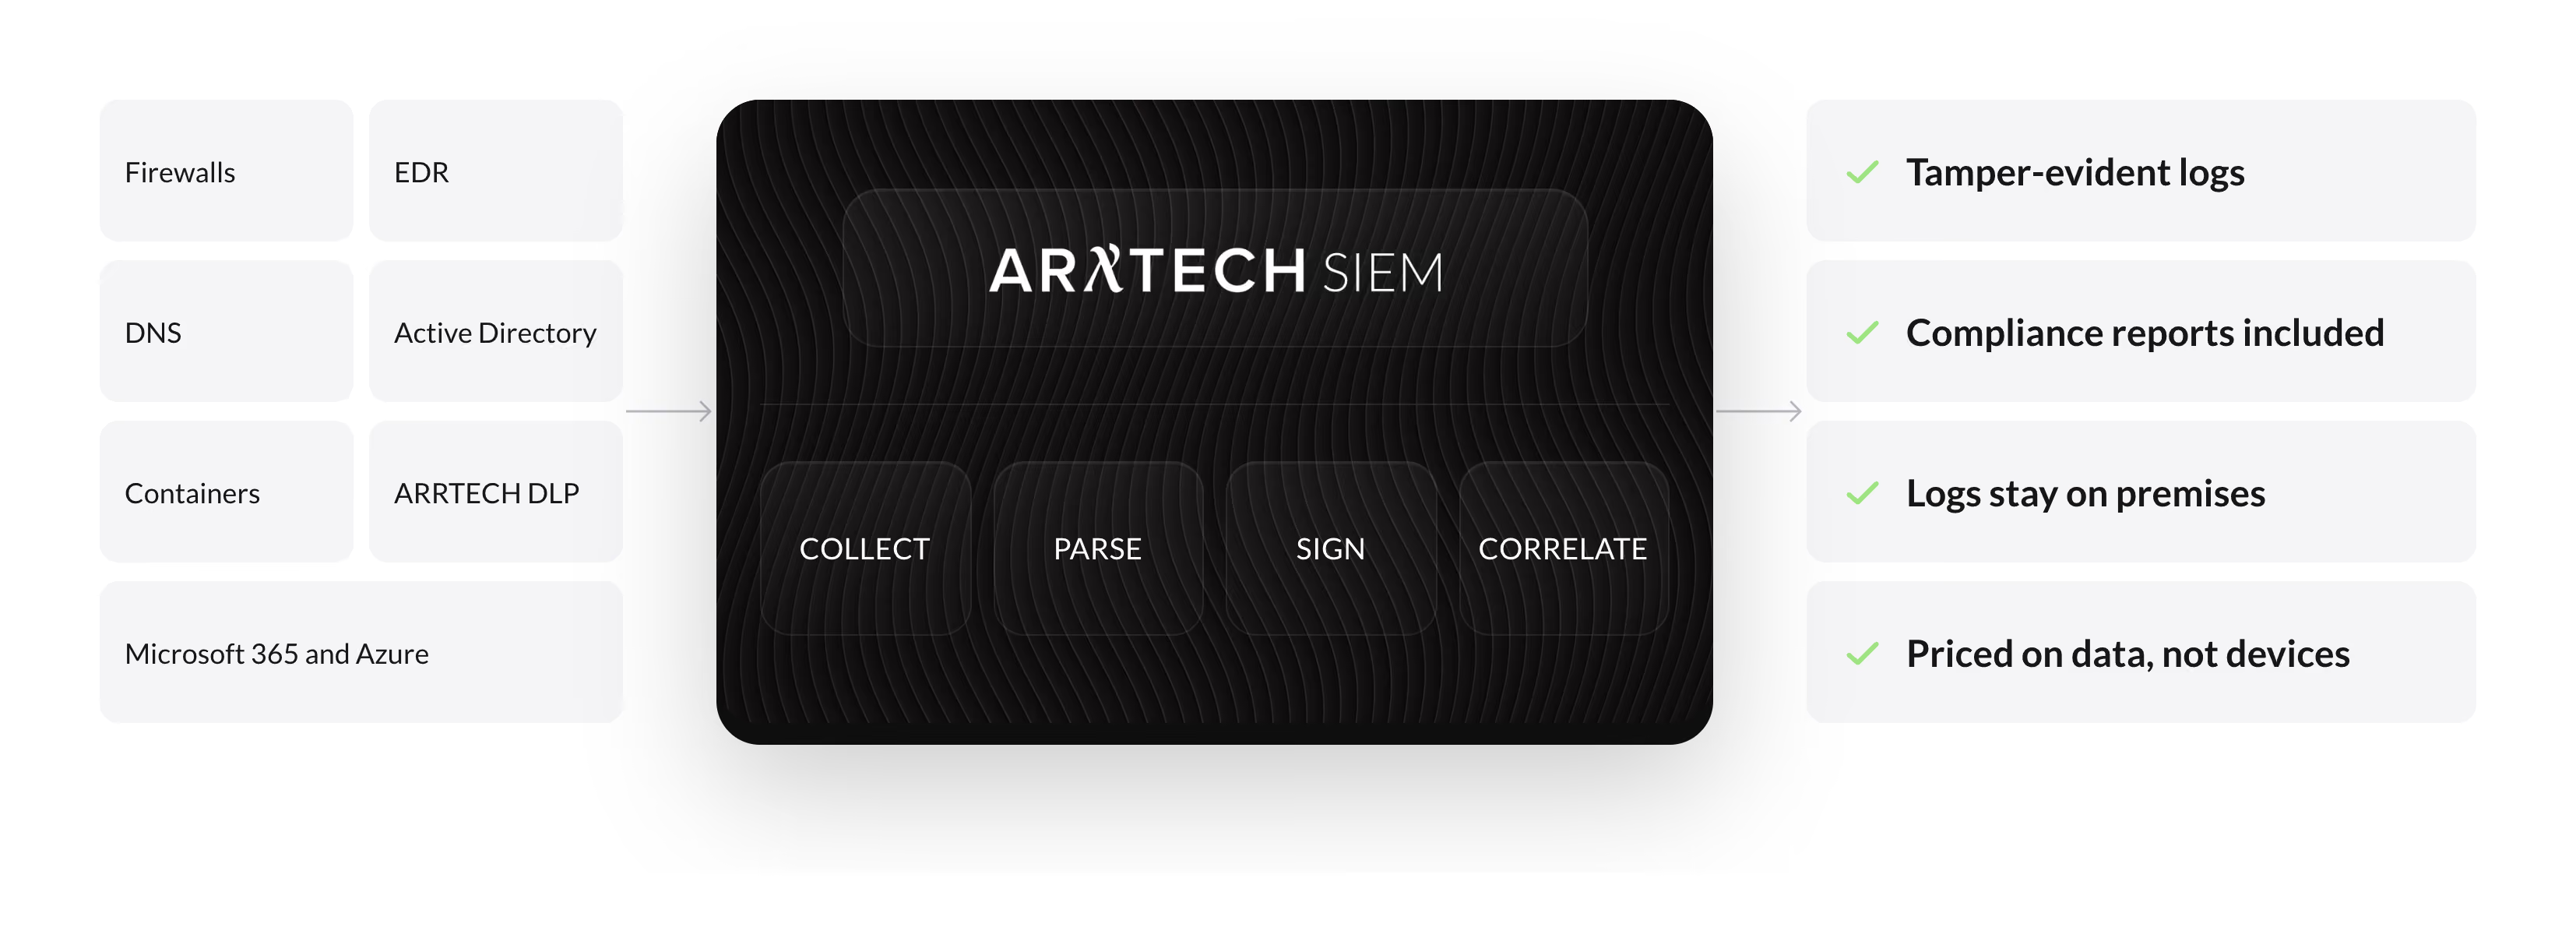
ARRTECH SIEM collects logs from firewalls, EDR, DNS, Active Directory, containers, ARRTECH DLP, and Microsoft 365 and Azure. It collects, parses, signs and correlates each one. The results: tamper-evident logs, compliance reports included, logs kept on premises, and pricing based on data volume.

What ARRTECH takes care of

ARRTECH SIEM keeps a signed record of activity across connected systems, on the organization's own servers. After an incident, the team can show regulators, auditors and insurers what happened, and they can verify the record without ARRTECH. Licensing follows data volume, with no charge per source or device, so the cost stays predictable.

Talk to our security team.

Prefer email? Write to info@arrtech.ai and we will reply within one business day. Partners and resellers can start here.

Product comparisons, documentation and other materials are available on request.

Choose a time for a call. We will look at the environment together, show where ARRTECH fits and answer questions.

ARRTECH

© 2026 ARRTECH Corporation. All rights reserved.