Skip to content
ARRTECH SOAR

Incident response automation with approval steps

ARRTECH SOAR turns a team's existing response steps into repeatable playbooks, through the security tools already in place.
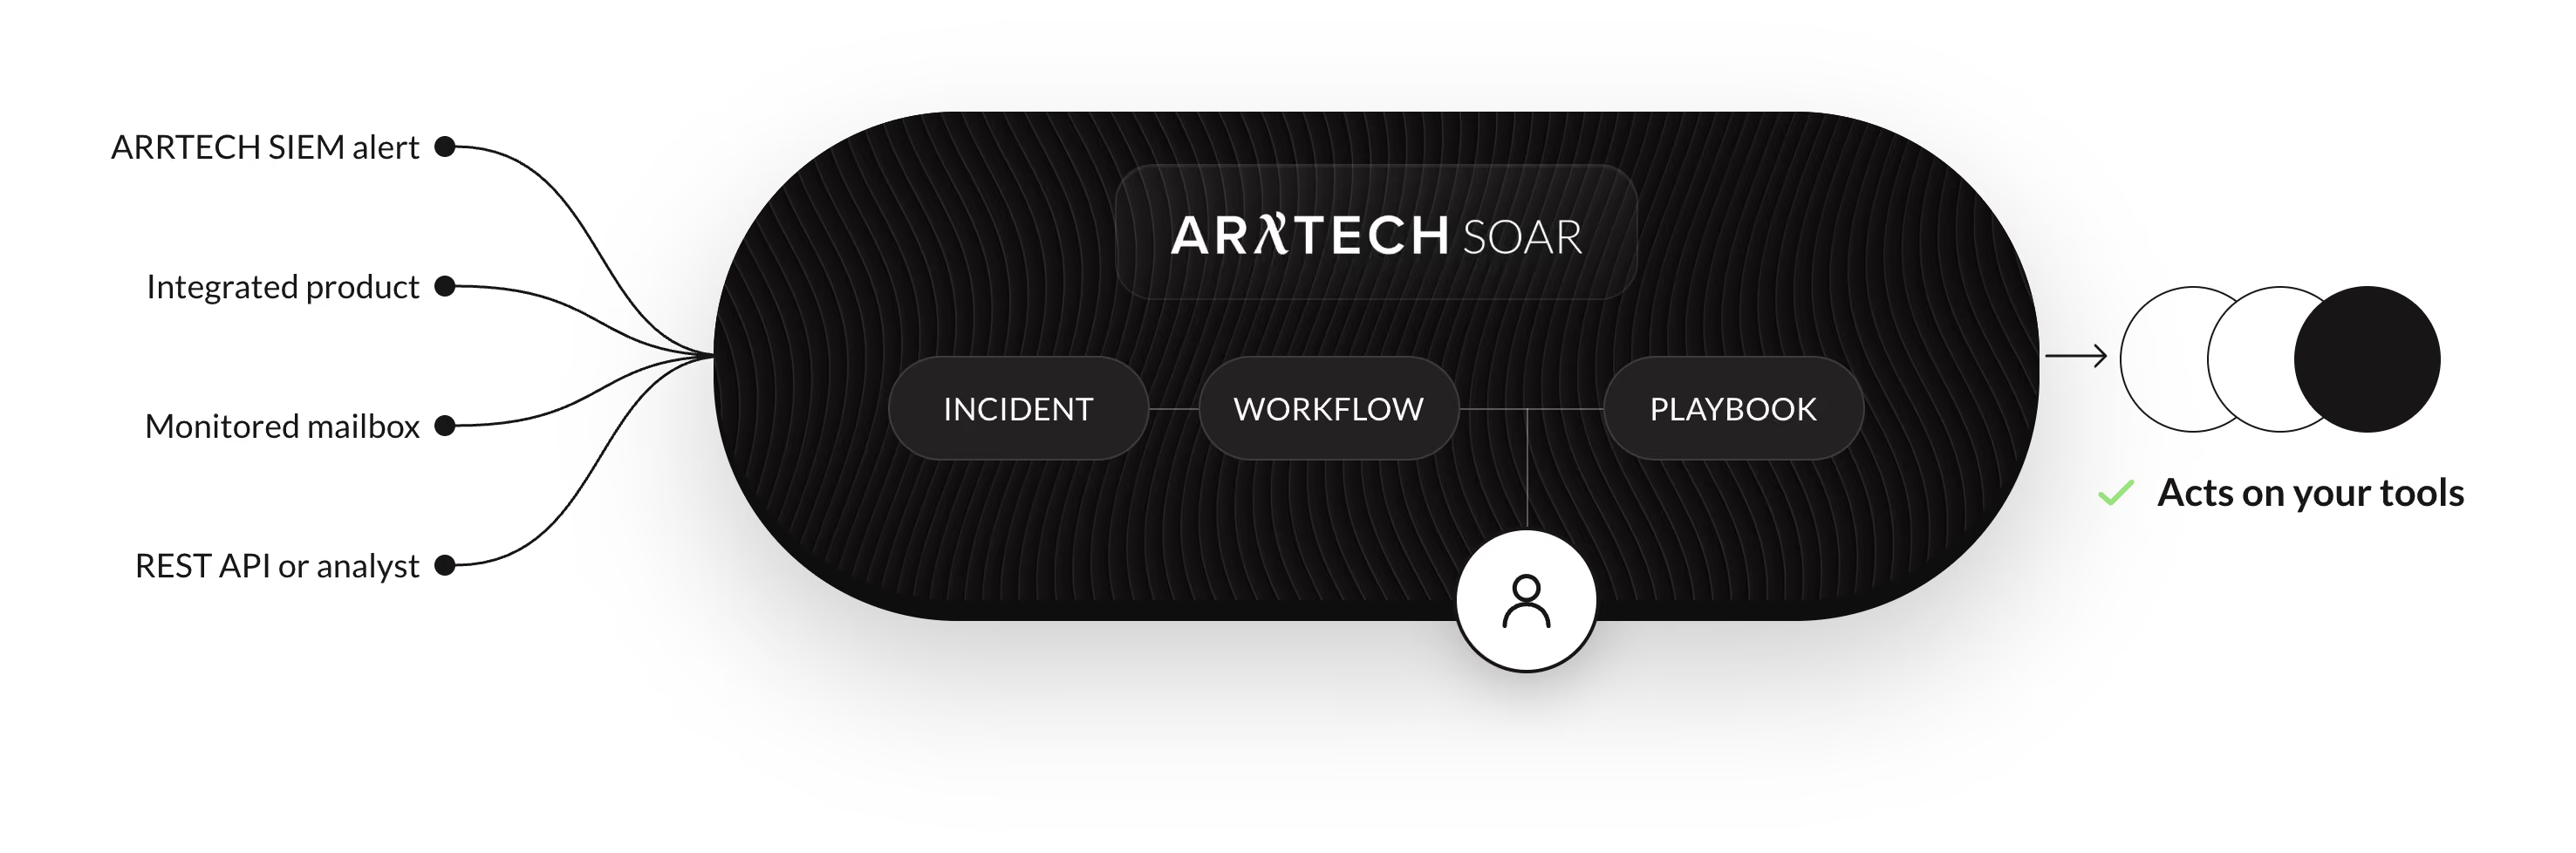
ARRTECH SOAR takes incidents from an ARRTECH SIEM alert, an integrated product, a monitored mailbox, the REST API or an analyst. Each incident runs a workflow and a playbook, with a person at the steps the team sets, and the playbook acts on the organization's tools.
From intake to record: the playbook acts on connected tools, and each step the team reserves goes to a person.

What ARRTECH takes care of

ARRTECH SOAR gives each shift a consistent response process. Routine steps run automatically, so a lean team handles more incidents and spends its time on judgment. Every run and every approval is recorded, ready for the board or a regulator after an incident.

Talk to our security team.

Prefer email? Write to info@arrtech.ai and we will reply within one business day. Partners and resellers can start here.

Product comparisons, documentation and other materials are available on request.

Choose a time for a call. We will look at the environment together, show where ARRTECH fits and answer questions.

ARRTECH

© 2026 ARRTECH Corporation. All rights reserved.