The AI layer of the ARRTECH Security Suite
AI detection and investigation that reads SIEM data
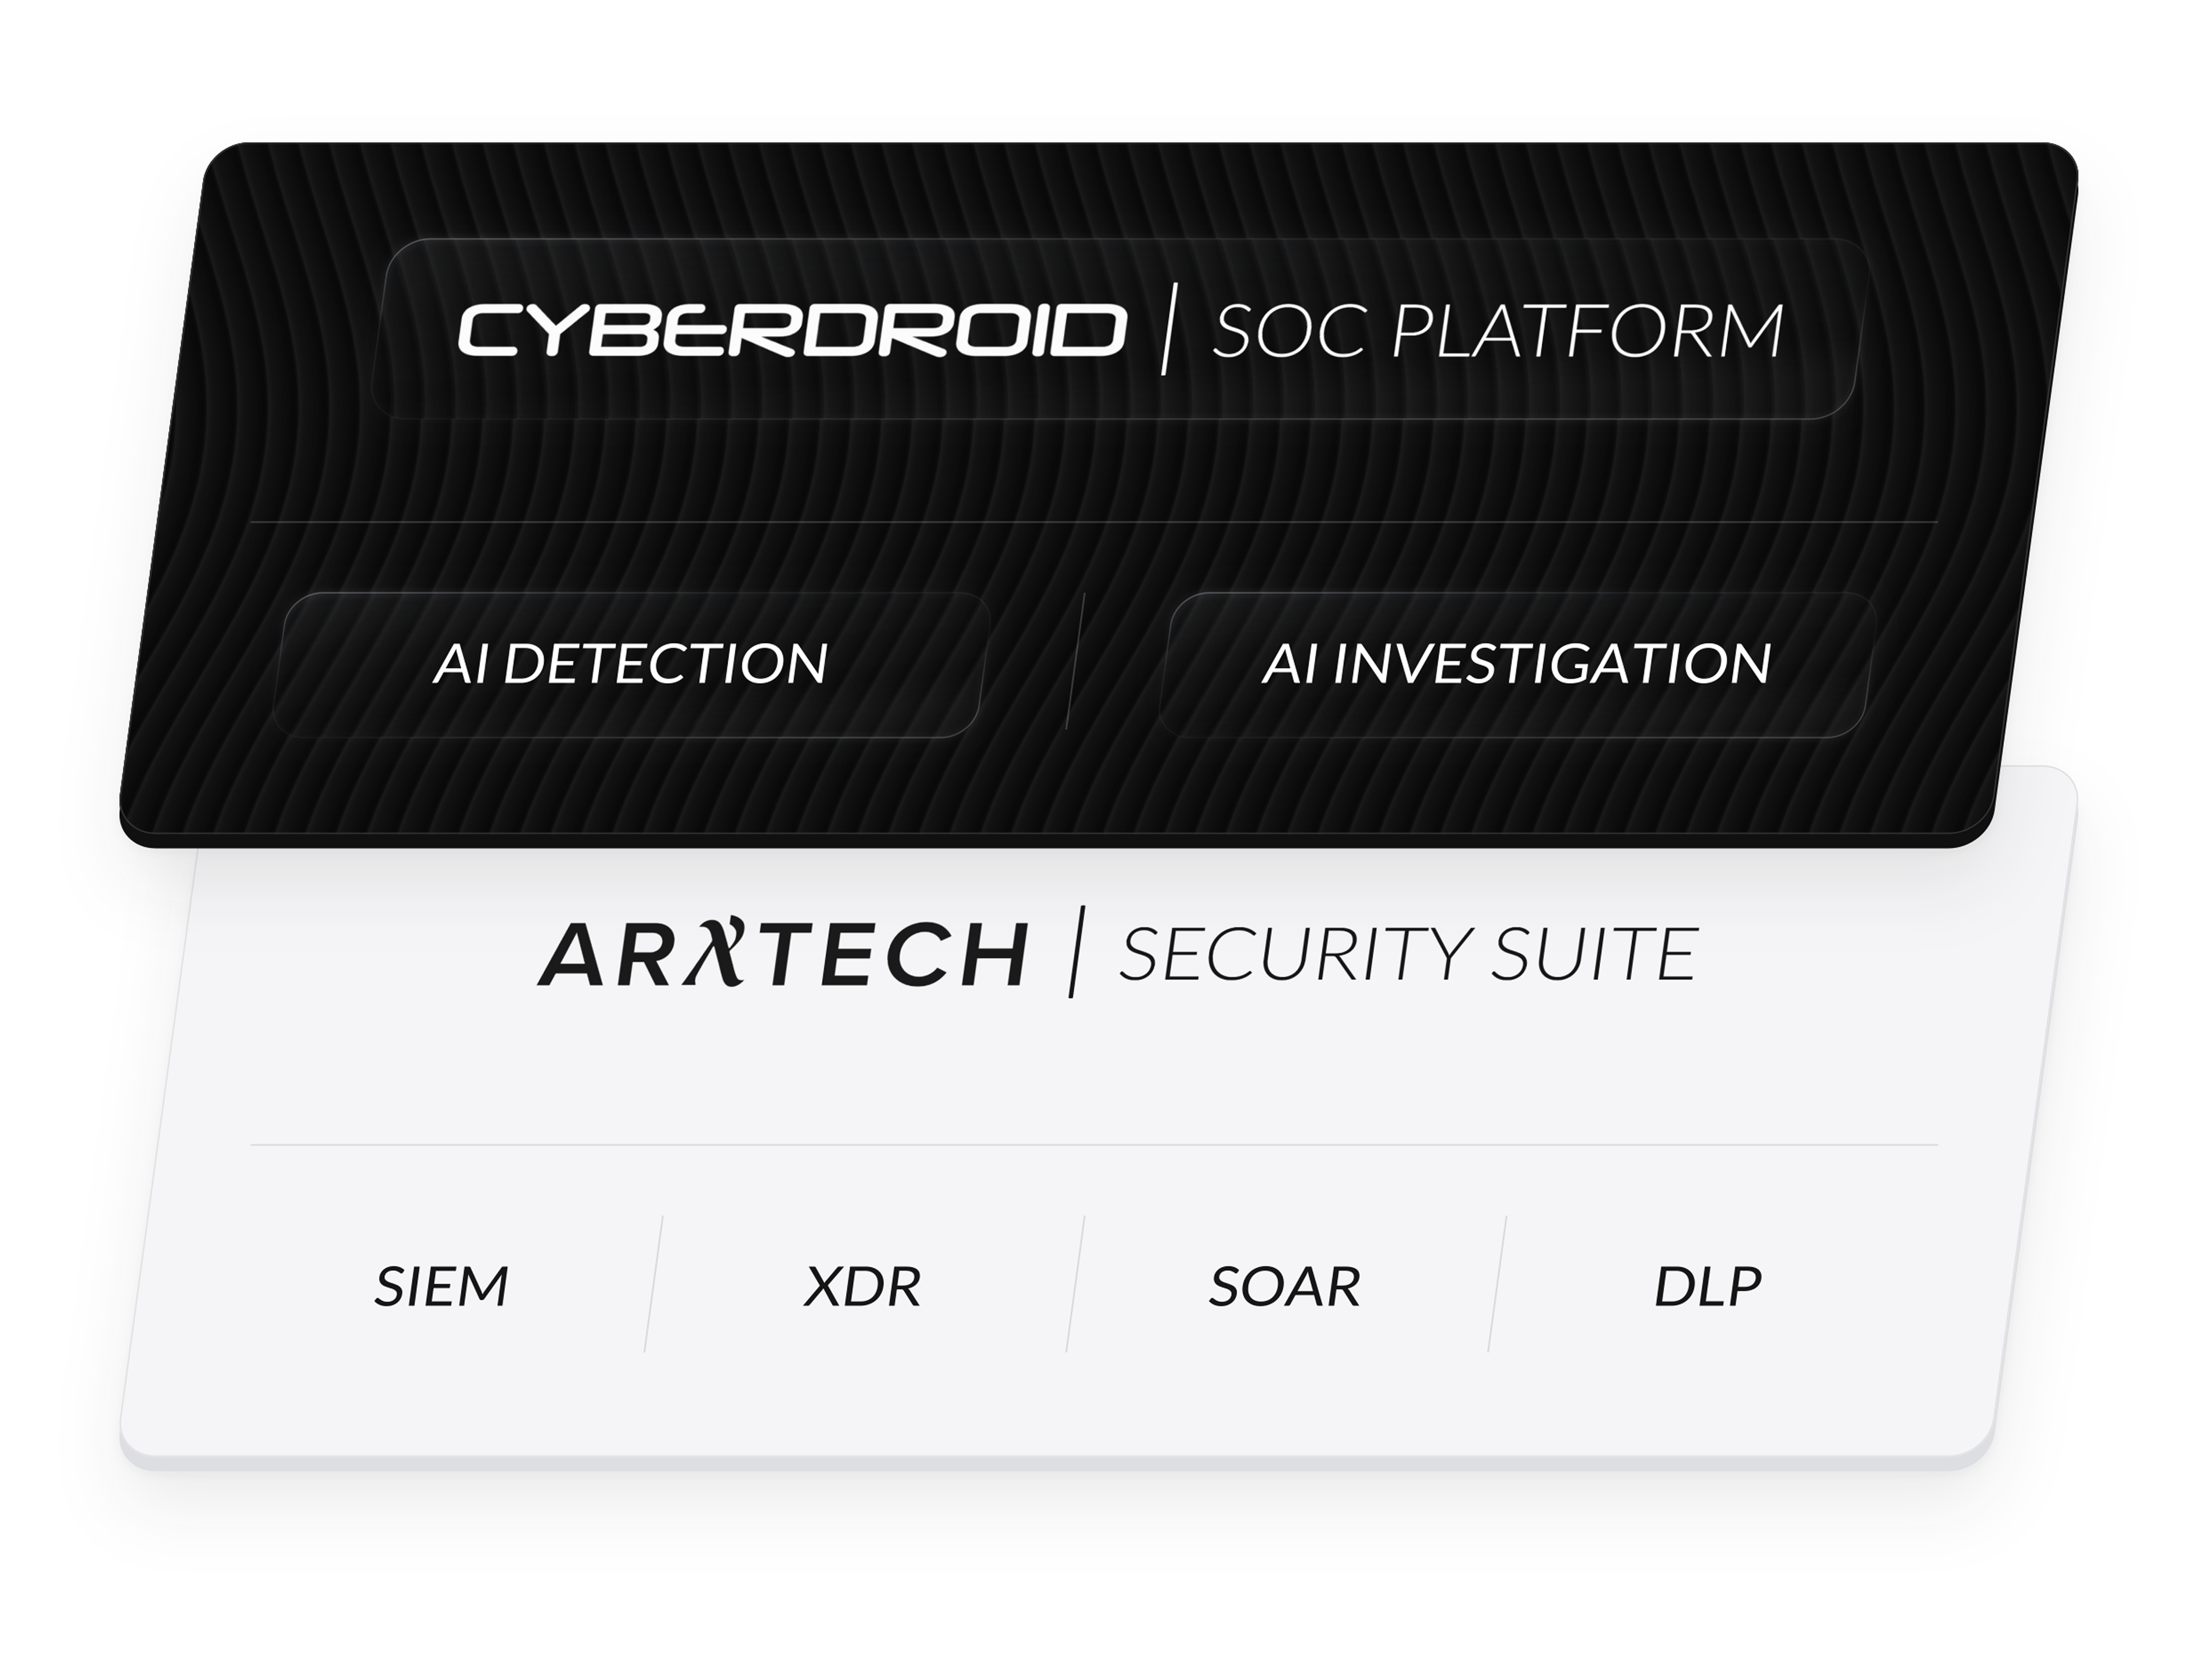
Cyberdroid gets more value from the SIEM the organization already pays for, with no software on endpoints. It finds unusual behavior, investigates it and writes each case with its evidence, verdict and next steps.
AI layer
Works on data the SIEM already collects
Cyberdroid reads an approved export of data the SIEM already collects, with no software on endpoints.
Behavioral detection alongside rules
SIEM rules identify activity that matches configured patterns. Cyberdroid AI Detection, available now to select organizations, compares each user, host and application with its own history and peers.
Findings and alerts written up as cases
Cyberdroid AI Investigation, in early access, takes a Detection finding or a SIEM alert and gathers the evidence. It writes a case with a verdict, rationale, evidence and next steps for an analyst to accept.
Accepted cases run through existing playbooks
Cyberdroid investigates and writes the case for analyst review. Response is a separate decision: ARRTECH SOAR runs the team's playbooks under the permissions and approval steps they have set.
Answers limited to approved teams
Investigation results often contain sensitive data. Policy sets which teams can ask Investigation questions and see its answers.
Products

Finds changes in behavior that predefined rules miss, connecting the signs of an attack so teams can understand what warrants action.

Investigates alerts, tests explanations and prepares the evidence, giving analysts more capacity while people retain authority over the response.